Disclaimer: This article is a personal technical study note. Any operations described should only be performed in authorized environments. Users bear full responsibility for any misuse.
This material is presented for study and discussion only; any illegal use of the technology is prohibited and the consequences rest with the user.
The environment setup steps are omitted here and can be found in the upstream project documentation. The article is relatively long because it walks through the whole experimental process.
The technique discussed here is not new, and OpenBTS was already capable of submitting short messages when the original notes were written. The article was written with two aims: to verify, in a controlled laboratory setting, whether short messages can still be observed on the air interface, and to review the architecture of GSM networks in the process. Corrections are welcome if any statement is inaccurate.
What about GSM
GSM, or Global System for Mobile Communications, is a cellular network with each cell having its own coverage area.
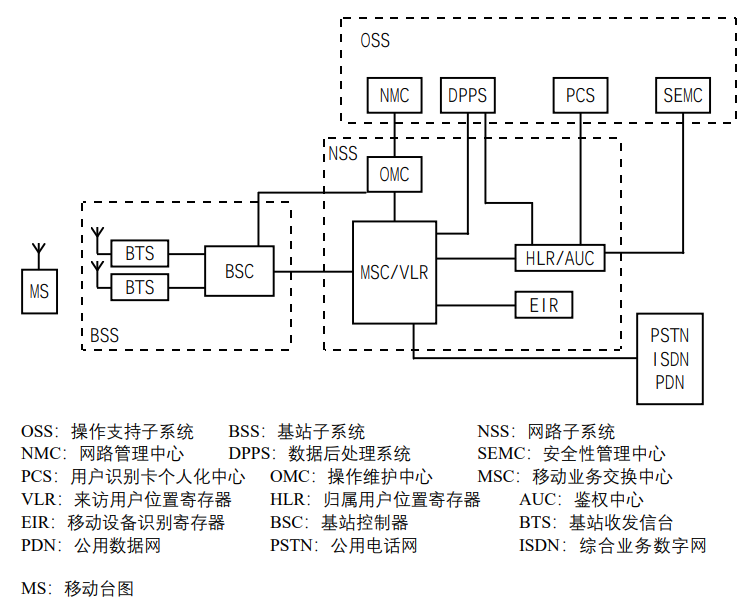
The basic GSM system consists of the OSS (Operations and Maintenance Subsystem), BSS (Base Station Subsystem), and NSS (Network Subsystem). Each subsystem provides a number of services, such as ISDN, PDN, PSTN and DPPS. Only the components relevant to the air interface and to subscriber identity are described briefly below; the network architecture itself is documented in the standard references.
Related Information:
- SIM (Subscriber Identity Module)
This is a card conforming to the ISO standard, the one inserted in your phone. It contains all user-related and radio interface information. A SIM card is required to use a mobile station. Emergency calls can be made without a SIM.
- BTS (Base Transceiver Station) and BSC (Base Station Controller)
The BTS is the radio portion of the BSS (Base Station Subsystem) and is controlled by the BSC (Base Station Controller). It typically serves the transceiver equipment in a cell and handles the switching between the BSC and radio channels.
- MSC (Mobile Switching Center)
The MSC is a node that controls multiple BSCs. It is the core equipment in the GSM system and has multiple functions.
- HLR (Home Location Register) and VLR (Very User Location Register)
The VLR serves mobile users within its control area. It stores information about registered mobile users within the control area and provides the necessary conditions for connected users to make calls.
The HLR is the central database for GSM, storing data related to all mobile users controlled by the HLR. An HLR can control several mobile switching areas. Important static data for all mobile users is stored in the HLR, including mobile subscriber identification numbers, access capabilities, subscriber categories, and supplementary services.
- EIR (Equipment Identity Register)
The EIR stores the IMEI of mobile devices. By checking against three tables—a white list, a black list, or a gray list—the EIR lists the IMEIs that are permitted, those that require monitoring due to malfunction, and those that are prohibited from use if stolen.
- AuC (Authentication Center)
AUC is primarily responsible for security measures, ensuring the confidentiality of voice data and signal information over the wireless network.
For information on the GSM ciphering algorithms (the A5 family), refer to the public literature; they are not covered in detail here. From a defensive standpoint the relevant property is that ciphering applies only to the air interface between the handset and the cell it is currently camped on, that the identifier exchanged during attachment is not protected by it, and that several A5 variants have been publicly analysed and are not considered strong. A terminal that falls back to 2G therefore loses the confidentiality guarantees that later generations provide.
回到正题:终端为何会失去短信的保密性?原因在于小区选择依据的是信号强度与网络广播参数,终端不会要求网络证明自身身份。终端在覆盖范围内总是优先接入信号更强的小区;若使用降频设备迫使终端回落至 2G,则 SMS 在空口上仅受当时协商的加密算法保护,而该保护强度有限,短信内容因此存在被截获的可能。

Pre
Hardware:
- Moto C118 (a low-cost Calypso-based handset, used here as the firmware target)
- USB to TTL 2.5mm cable
- CP2102 module
Software:
- osmocom-bb(https://osmocom.org/projects/baseband)
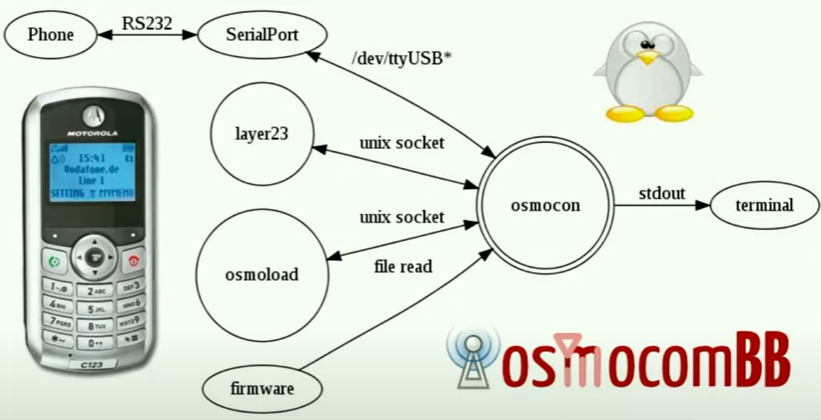
Regarding the osmocom-bb project, this is an open source GSM protocol project, which aims to achieve three-layer implementation from physical layer 1 to layer 3 on the mobile phone side.
- OpenBTS-5
- GNU ARM cross toolchain
Build
The build was carried out on Kali Linux. The system should be updated first, and the host-side build dependencies installed, so that the toolchain step does not fail at link time:
1 | apt-get install build-essential libgmp3-dev \ |
The baseband firmware runs on an ARM core, so an arm-none-eabi cross-compiler is required. It is built from the GNU binutils, GCC and newlib source trees using the gnu-arm-build.3.sh helper that the project publishes; the script asks for the prefix, source and build directories before it starts and confirms when the compiler has been produced. The resulting bin directory is then added to PATH in ~/.bashrc.
1 | export PATH=$PATH:<YOURPATH>/install/bin |
The osmocom-bb sources are then obtained from the project repository, together with the libosmocore library they depend on. libosmocore is built and installed first (autoreconf, configure, make, make install, followed by ldconfig), and the firmware and host tools are built afterwards from the src directory. The steps are summarised here rather than reproduced in full; the authoritative procedure is the upstream project documentation.
If the build fails with insufficient permissions or missing libraries, the error message names the package that has to be installed, as shown below.
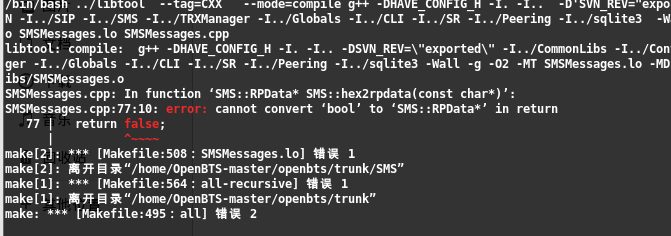
A missing package can also produce the error below, in which case the named package is what needs to be installed.
Air-Interface Observation in a Controlled Environment
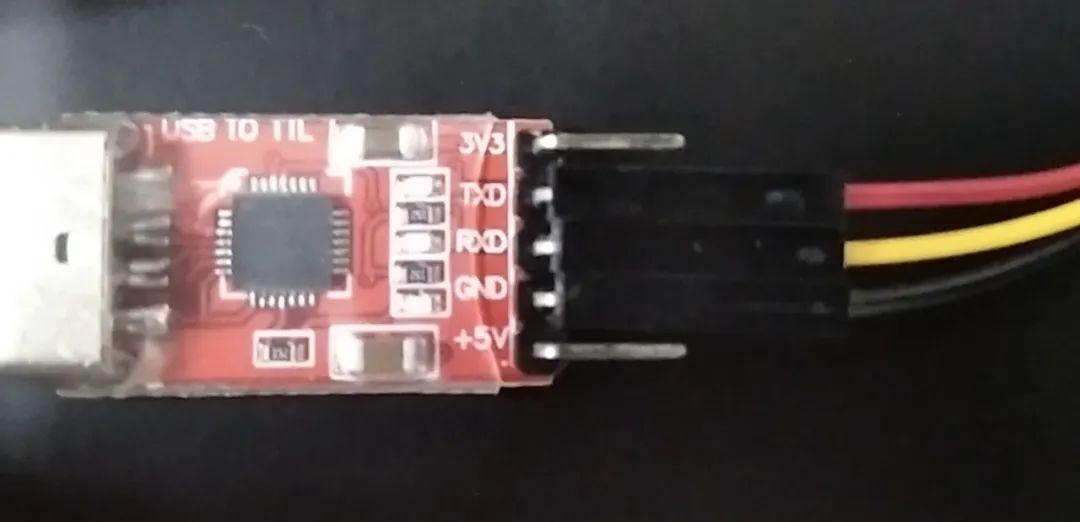
The observation setup consists of the handset running the osmocom-bb firmware and a host application that talks to it over the serial link. The firmware replaces the stock baseband software, which is what allows the handset to report what it receives on the air interface instead of only serving its own subscriber profile; the host side then drives the handset and decodes the results. Assembly-level details of the cable and of the firmware-loading procedure are omitted here.
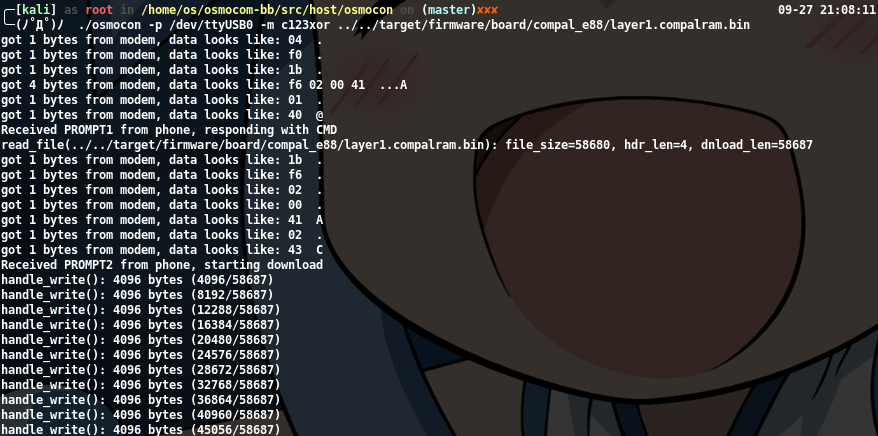
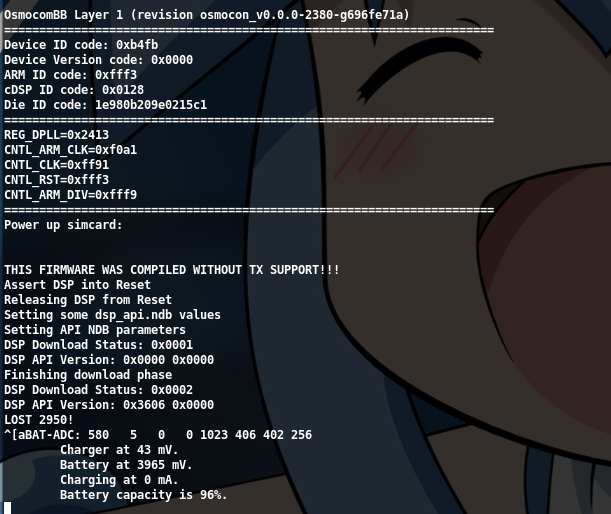
Once the firmware has been loaded, the handset reports its layer-2/3 state and accepts control from the host over the same serial link. The unit used for these notes has had its display removed, so the layer-2/3 state shown on screen after loading could not be photographed; the loading output captured on the host side is shown below.
The first step in the experiment is a survey of the surrounding cells. The osmocom-bb host tools provide a cell-logging application that reports, for each detected channel, the channel number and the received power, together with the network identity broadcast by that cell. A representative line has the following fields:
1 | Cell: ARFCN=<channel> PWR=<dBm> MCC=<mobile country code> MNC=<mobile network code> |
Among them, PWR is the received signal strength, where a smaller value corresponds to a stronger signal, and ARFCN is the absolute radio frequency channel number of the cell.
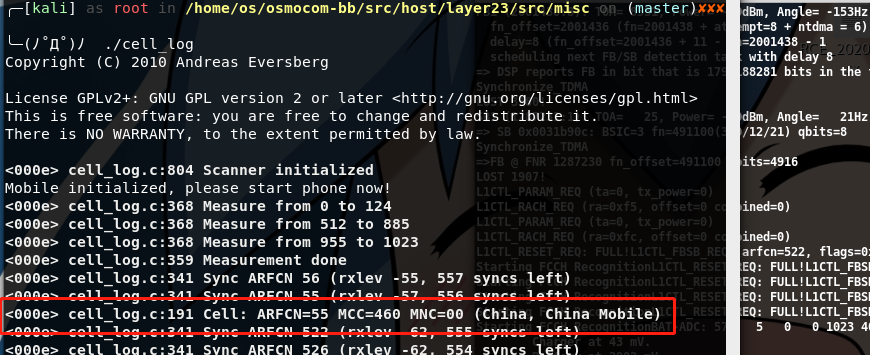
The second step selects one of the surveyed channels and follows its broadcast control channel, which is how the system information of that cell is collected.
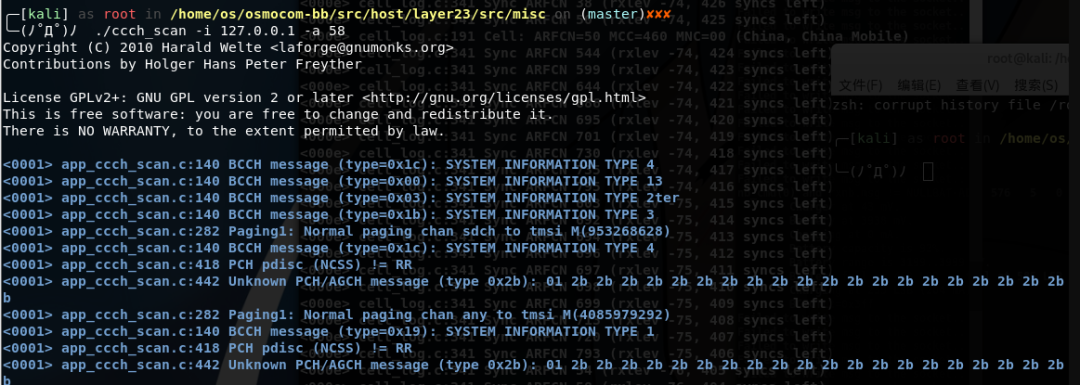
If output continues to scroll, the host is receiving the broadcast channel of the selected cell.
For information on GSM frequency bands, refer to the chart below.
| Frequency Band | Name | Channel Number | Uplink (MHz) | Downlink (MHz) | Other |
|---|---|---|---|---|---|
| GSM 850 | GSM 850 | 128 - 251 | 824.0 - 849.0 | 869.0 - 894.0 | United States, South American countries, and parts of Asia. |
| GSM 900 | P-GSM 900 | 1-124 | 890.0 - 915.0 | 935.0 - 960.0 | This is the first frequency band implemented by GSM and is also the most widely used. |
| E-GSM 900 | 975 - 1023 | 880.0 - 890.0 | 925.0 - 935.0 | 900 MHz extended band | |
| R-GSM 900 | n/a | 876.0 - 880.0 | 921.0 - 925.0 | Railway GSM (GSM-R), a special version developed for railway dispatching communication systems. | |
| GSM1800 | GSM 1800 | 512 - 885 | 1710.0 - 1785.0 | 1805.0 - 1880.0 | Suitable for markets with high channel capacity requirements, second only to 900 MHz in application scope. |
| GSM1900 | GSM 1900 | 512 - 810 | 1850.0 - 1910.0 | 1930.0 - 1990.0 | Mainly used in America. Due to frequency overlap, it is incompatible with the 1800M system. |
Source: http://www.blogjava.net/baicker/archive/2013/11/13/406293.html
The traffic captured in this way can be decoded with the gsm_sms protocol dissector in Wireshark, which reconstructs the short-message payloads and makes their content directly readable.

This is the step that turns an air-interface observation into readable content, and it is the reason the confidentiality of a short message on 2G is bounded by the air interface rather than by the messaging application: no key management or application-layer protection is involved.
As noted above, 2G services in the region where these notes were taken have largely been decommissioned. That materially changes the risk: a downgrade has to be induced before any of the above becomes relevant, and a terminal that never camps on a GSM cell is not exposed through this path. The defensive problem is therefore a migration problem, and it is examined in the last section.
Extension
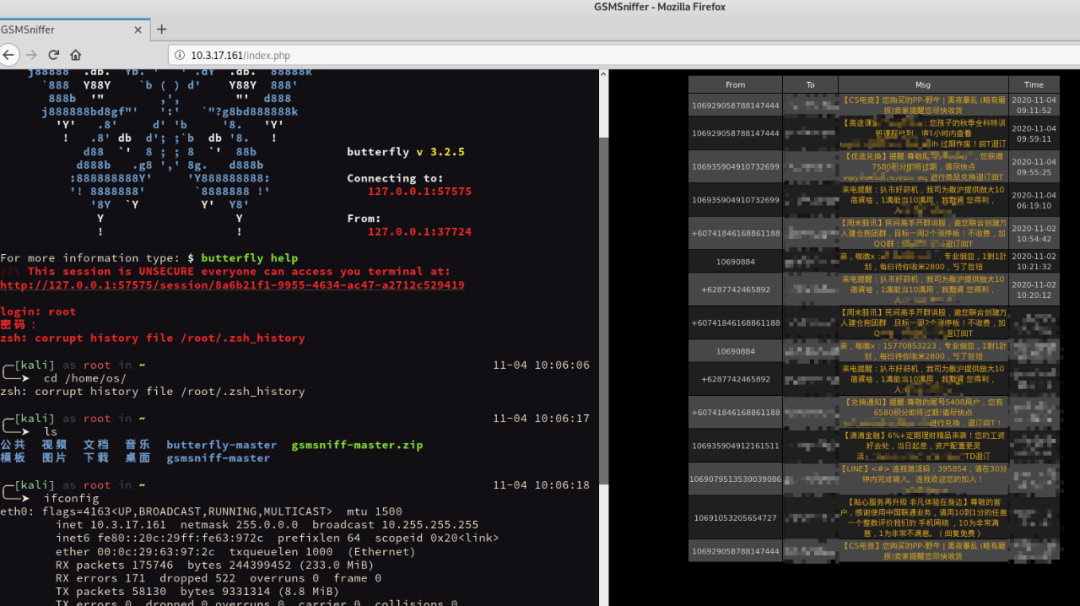
Public projects exist that automate the entire chain — firmware loading, cell survey, message capture and storage in a database, with a web interface for browsing the results, built on a conventional stack (Tengine, PHP, MySQL). Their engineering significance is that the collection pipeline becomes scripted end to end, which lowers the operational barrier for anyone who has the hardware.
The implication for defenders is direct. The difficulty of the technique cannot serve as a control, because the tooling is public and packaged; and because captured content is written to a queryable store, that store holds personal data and carries its own retention and protection obligations.
Defence
- Prevent the downgrade to 2G. Configure the handset to 4G/5G only, or to a mode that keeps GSM disabled; on several platforms the same option is reachable through the engineering or service menu. The effectiveness of this control depends on the local network: where an operator still runs a 2G layer the fallback remains possible, and where the layer has been retired there is nothing for the terminal to fall back to.
- Treat short messages as an untrusted channel for authentication. A one-time code carried over SMS inherits the security of the serving network, so an account protected only by such a code remains recoverable by anyone able to observe the air interface. TOTP applications, push-based approval or hardware security keys should be the default second factor, with SMS restricted to cases where the risk is genuinely low.
- Observe the terminal-side indicators. A sudden drop of the network indicator to G, an unexpected network name, an abrupt change in signal strength, or unusual delays in message delivery are each weak signals on their own, but their combination is worth investigating, and a device that reports an insecure connection should be treated as such.
- Detect at the network layer. Over-the-air equipment produces counters that are visible to the operator without any agent on the terminal: location-update and attach rates that deviate from the planned radio footprint, cells that do not belong to the network plan, and ciphering-algorithm downgrades. These are the primary means of locating unauthorised transmitters.
- Do not build business availability on SMS. Notification and approval flows that depend on short-message delivery inherit the same air-interface risk. Where such a flow cannot be replaced, the message content should not carry anything that is sensitive by itself.
Legal and Data-Protection Boundary
An experiment of this kind is only defensible inside a defined legal boundary, and the boundary is worth stating explicitly:
- Authorisation first. Spectrum use is licensed in mainland China under the Radio Regulation of the People’s Republic of China, and setting up or operating a radio station without approval is unlawful. Interest in the technology is not a substitute for authorisation.
- Shielding and isolation. The receiver and any transmitter should be operated inside a shielded enclosure or connected to a dummy load, so that no signal reaches handsets outside the laboratory and no interference is caused to commercial networks.
- Scope of the experiment. Only laboratory devices and consented participants should be involved. Attracting nearby handsets is outside the scope of a controlled experiment even when the objective is defensive.
- Handling of captured content. Captured messages and decoded payloads are personal data. They should be minimised, stored under access control, retained only for the period the analysis requires, and redacted before publication. The database-backed collection systems described above are, for this reason, themselves sensitive systems that need the same protection as any other store of personal data.
Legacy access technologies remain a productive target for research, and publicly reported competition work has demonstrated attacks against LTE small cells. The durable conclusion from this experiment is that the effective control is migration rather than obfuscation: as long as terminals can be pushed back onto a legacy air interface, the protections of the current generation do not apply to them.


